What a Capture the Flag Is
From Illustrated Hacking
Who it is for: Beginners exploring capture-the-flag challenges in authorized practice environments.
Working manuscript · 2027–2028 Edition. The full book is forthcoming; text and illustrations may change.
A capture-the-flag competition presents security challenges inside an authorized environment. Each challenge asks a player or team to recover a secret string called a flag. Submitting the expected string to the scoreboard records a solve and awards points according to the event's rules.
The challenge description defines the intended target: perhaps a supplied file, a temporary web application, or a network service created for the event. Permission is limited to that target and the methods allowed by the rules. The scoreboard, hosting platform, other players, and unrelated systems remain outside scope.
CTF organizers usually isolate challenge data from production systems, but no online platform can promise that risk is literally zero. Follow the event's rules, avoid unnecessary traffic, and report unexpected platform defects through the stated channel rather than testing them further.
Read the chapter
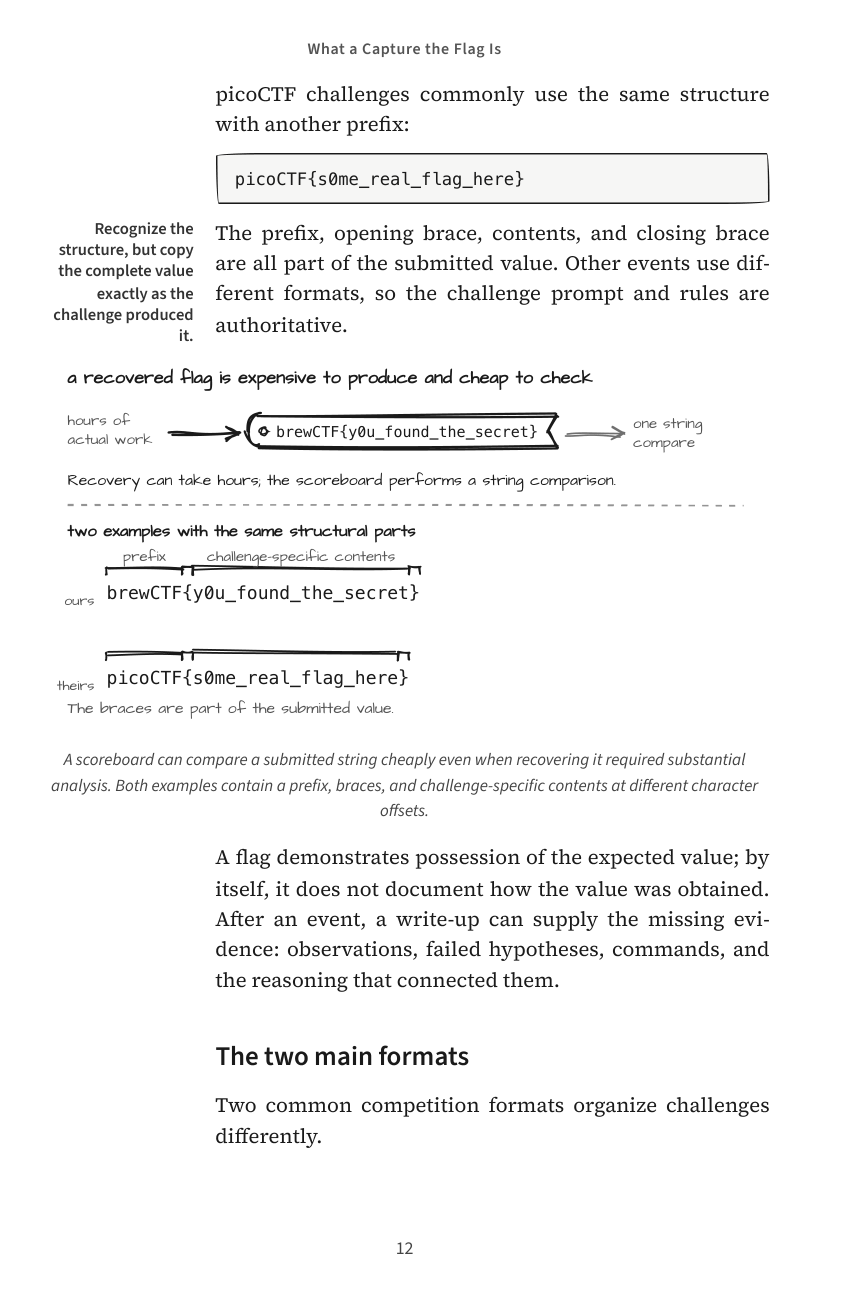
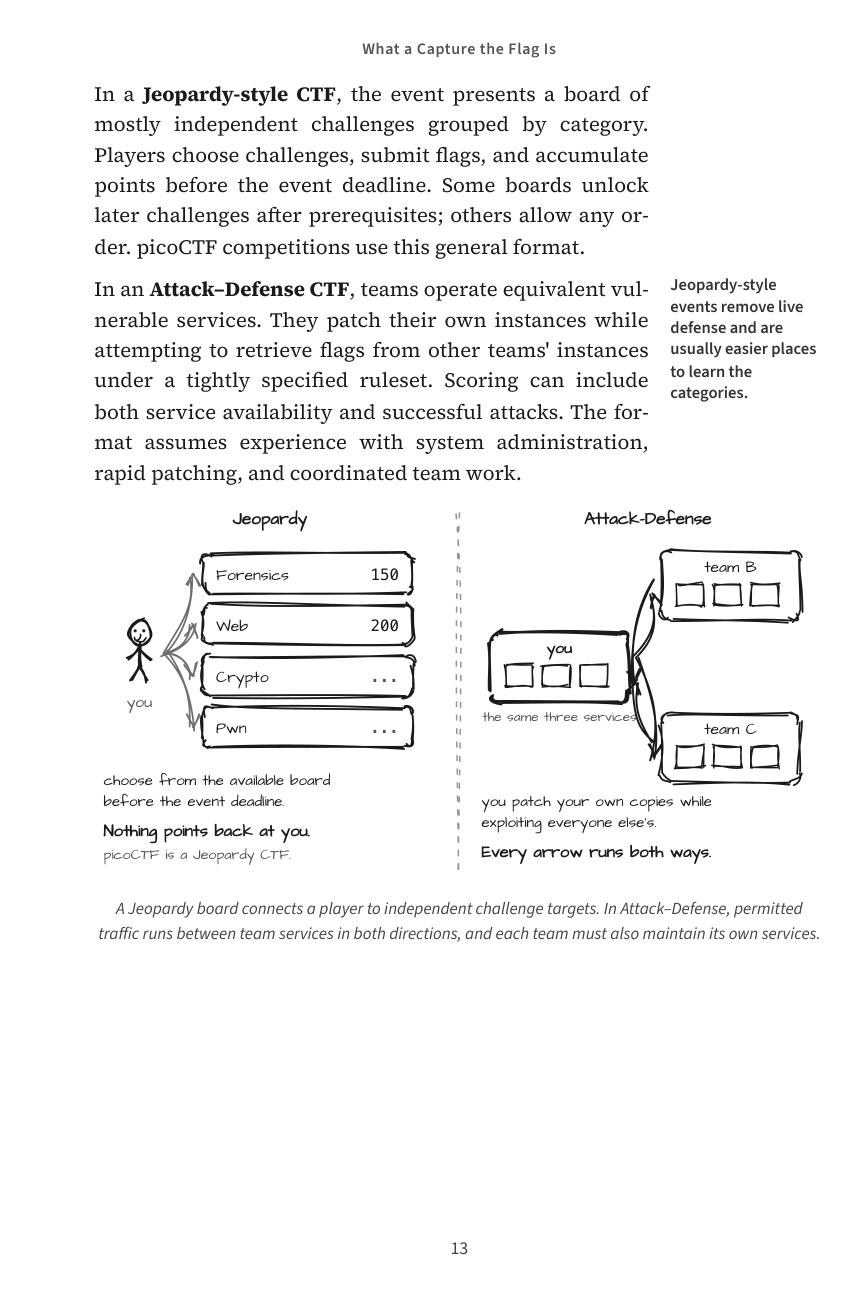
The preview below shows the first 3 pages. The PDF contains the complete 8-page chapter, with selectable text and the original illustrations.
Download sample chapter (PDF) ↓Open PDF in a new tab ↗
Keep exploring Illustrated Hacking
Learn security through a fictional practice lab. Pair each vulnerability with the defensive idea that prevents it.
See the book outline →Questions or corrections? support@hackerbrewery.com